
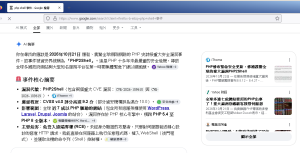
事件核心摘要
漏洞代號:PHP2Shell(包含兩個重大 CVE 漏洞:CVE-2026-109618 與 CVE-2026-109619)。
嚴重程度:CVSS v4.0 評分高達 9.2 分(部分資安機構評為滿分 10.0)。
影響範圍:全球 近 7 成以 PHP 驅動的網站(包含所有底層架構使用 WordPress, Laravel, Drupal, Joomla 的站台),漏洞存在於 PHP 核心引擎中,橫跨 PHP 5.4 至 PHP 8 全版本。
主要危害:免登入遠端奪權 (RCE)。未經身分驗證的攻擊者,只要對伺服器發送精心設計的惡意 HTTP 請求,就能直接在伺服器上執行任意程式碼、植入 WebShell(後門程式),並獲取主機的命令列(Shell)控制權。
維京電訊在 22-OCT-2026 3:56 HKT (GMT +8) 已經完成各服務器更新.
網路安全, 網路管理員有盡大責任, 一定要及時打補丁, 維京電訊致力提供穩定的網路服務, 盡心為你最到最好 😉
Core Event Summary
Vulnerability Code: PHP2Shell (includes two major CVE vulnerabilities: CVE-2026-109618 and CVE-2026-109619).
Severity: CVSS v4.0 score is as high as 9.2 (rated a maximum of 10.0 by some cybersecurity organizations).
Impact Scope: Affects nearly 70% of PHP-driven websites worldwide (including all sites built on underlying frameworks like WordPress, Laravel, Drupal, and Joomla). The vulnerability exists within the PHP core engine and spans all versions from PHP 5.4 to PHP 8.
Primary Threat: Unauthenticated Remote Code Execution (RCE). An unauthenticated attacker can execute arbitrary code on the server, plant a WebShell (backdoor program), and gain command-line (Shell) control of the host simply by sending a carefully crafted malicious HTTP request to the server.
Viking Telecom completed updates across all servers on 22-OCT-2026 at 3:56 HKT (GMT +8).
Cybersecurity and network administrators bear a massive responsibility to apply patches in a timely manner. Viking Telecom is committed to providing stable network services and dedicated to doing our absolute best for you! 😉
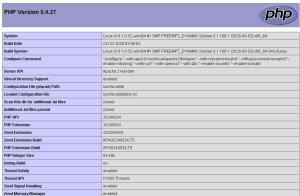
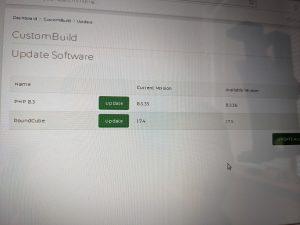
we also build the most updated apache
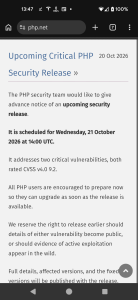
密切關注 php.net 官方網站預告推出重大保安漏洞補丁
Closely monitoring the php.net official website for the upcoming critical security patch announcement.
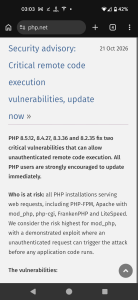
php.net 公告補丁已經推送, 我們馬上為各服務器打補丁
The security patch advisory has been officially released on php.net, and we are immediately deploying the patches across all of our servers.